Every day, we see ads everywhere.
On news sites. In apps. On social media. On videos. On search results. Most of us barely notice them anymore. We swipe past them, close them, or ignore them completely. They’ve become part of the background noise of the internet.
But what if one of those ads was not just selling something — what if it was part of a spyware attack?
That is the disturbing lesson from the Citizen Lab research on how Discover-Tech helped turn targeted advertising into a pipeline for spyware. In simple terms, the report shows that the online ad ecosystem can be abused in ways most people would never imagine. What looks like an ordinary ad can, in some cases, become a hidden path into your device. The result: surveillance without a click, without warning, and without the victim realizing it happened.
The Hook: Why This Should Matter to Everyone
We usually think of ads as a nuisance, not a threat.
They slow pages down. They follow us around. They guess what we might want to buy. Sometimes they’re creepy, but usually they seem harmless.
That’s exactly why this is so dangerous.
When a system is trusted and routine, it becomes easier to abuse. People stop paying attention. Security defenses are often built around the idea that danger comes from obvious things: suspicious files, strange links, fake login pages, malicious downloads. But this research shows that danger can also hide in the normal machinery of the internet itself.
In this case, targeted advertising was not just used to reach people — it was used as a delivery system for spyware. Citizen Lab says this was the first public technical confirmation of zero-click mercenary spyware delivered through targeted ads, a method it calls AdFection.
That means the attack did not rely on tricking someone into clicking a link or opening a file. The danger was embedded in the ad ecosystem itself.
How It Works — Without the Jargon
Let’s make this easy to picture.
Imagine the internet’s ad system as a giant digital highway with thousands of billboards.
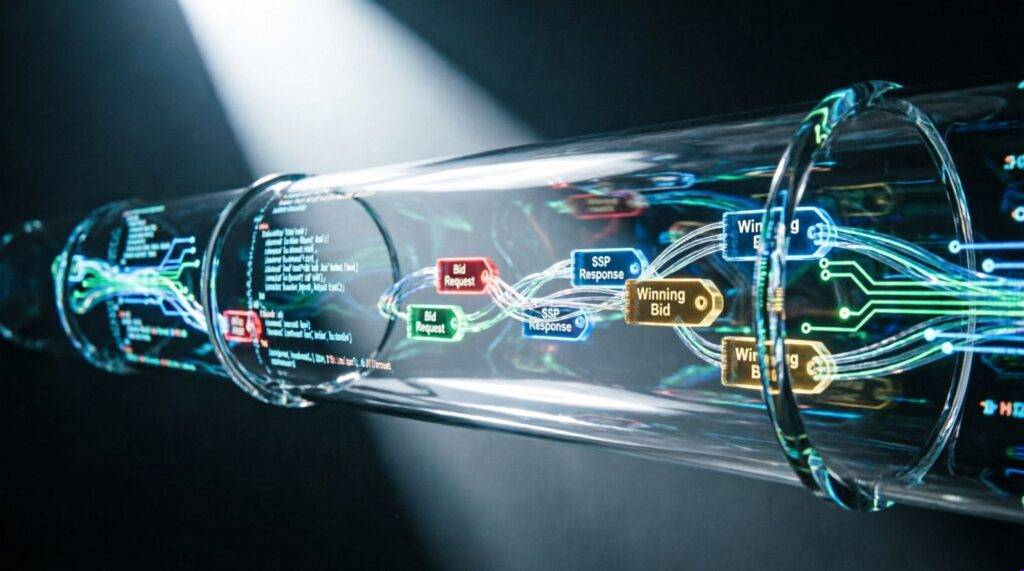
Every time you open a website or app, a tiny auction happens in the background. Different advertisers bid for the chance to show you something. The system decides, in a split second, which ad will appear. This process uses data about your device and browsing context so ads can be more “targeted.”
Now imagine one billboard company is dishonest.
Instead of just showing a normal ad, it uses the ad space like a secret tunnel.
Here’s the simplified version:
- You open a website or app.
- The app asks the ad system for an ad.
- The ad system shares details about your device so advertisers can target you.
- A malicious actor uses that system to identify a target.
- The ad loads like a normal ad.
- Behind the scenes, it triggers something dangerous.
- Spyware may be installed or the device may be compromised — sometimes without any click at all.
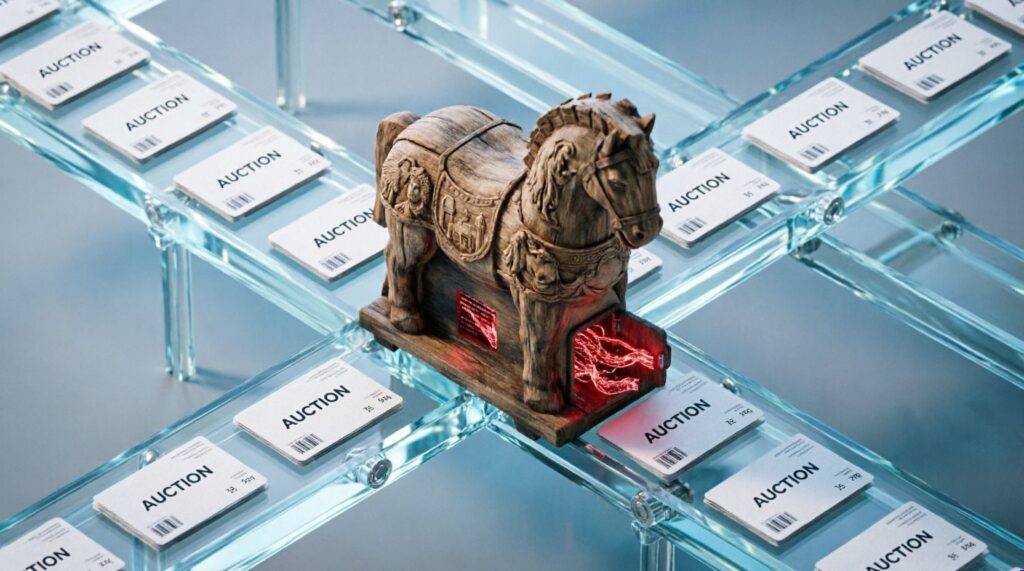
A good analogy is a Trojan horse.
From the outside, it looks like a harmless gift. Inside, it contains something harmful. The user thinks they are just seeing an ordinary advertisement, but the ad can act as a trap hidden inside a familiar system.
That is what makes this so unsettling: the attack blends in.
What Citizen Lab Found
The Citizen Lab report connects this abuse to a real-world spyware operation involving Candiru and devices at Al Jazeera. The researchers describe how Discover-Tech operated in a way that bridged the gap between the ad-tech world and spyware operators.
That matters because it shows spyware delivery is not always just about one shady app or one phishing email. Sometimes it grows out of the larger advertising ecosystem that powers much of the web.
The report also found that Discover-Tech’s ads were shown on nearly 200,000 websites and apps across many countries over just a four-month period, based on analysis of billions of ad-bidding records.
That scale is what makes this so alarming.
If a malicious actor can reach that many apps and sites through the ad stack, then the attack surface is enormous. It is not limited to one country, one news outlet, or one type of person. It can touch ordinary users who are simply browsing the web.
Why This Matters in Real Life
This is not just a story about one spyware case.
It is a story about how modern internet advertising can be turned into a surveillance tool.
If this kind of abuse exists, the consequences can be serious:
- Privacy loss: Your device, behavior, and interests can be mapped without your clear consent.
- Silent surveillance: Spyware can expose messages, contacts, location, photos, and more.
- Targeted intimidation: Journalists, activists, lawyers, and dissidents can be singled out.
- Broader risk to everyone: Even if you are not a high-profile target, the same ad systems are used everywhere.
- Trust erosion: People start losing confidence in the very websites and apps they use every day.
This is especially important because ad-tech is often treated as “just marketing.” But once ad systems can carry code, profile users, and route traffic through opaque intermediaries, they become part of the security problem too.
Who Is at Risk?
The short answer: almost everyone who uses apps and websites with ads.
But some people face higher risk:
- Journalists
- Human rights defenders
- Activists
- Political campaign staff
- Lawyers
- Researchers
- People handling sensitive personal or professional information
Citizen Lab warns that these kinds of attacks are especially concerning for groups that may already be under surveillance pressure.
At the same time, regular users should not assume they are immune. Attack infrastructure like this can spread widely, and the more common the system is, the more likely ordinary people are to be exposed at some point.
Why “Targeted” Ads Are a Bigger Problem Than They Look
The word “targeted” usually sounds harmless.
It just means an ad is trying to match your interests, right?
Not always.
To target ads, the system often collects and shares signals about your device, browsing context, app usage, or location-related data. That information may be used to decide which ad to show you, but it also creates a detailed map of who you are and where you are online.
That is useful for marketers.
It is also useful for attackers.
If someone can get into that system, they may not need to break through your front door. They may just walk through the ad network’s side entrance.
That is why this matters beyond the spyware case itself. It shows how business systems built for advertising can be repurposed for surveillance.
What Makes This Especially Dangerous
There are a few reasons this kind of attack stands out:
1. It blends in
A normal ad does not look threatening. People and systems often trust it by default.
2. It can be silent
No obvious warning. No dramatic pop-up. No “you’ve been hacked” message.
3. It can be highly scalable
Ad networks reach huge numbers of sites and apps.
4. It can bypass common caution habits
People are taught not to click suspicious links. But what if the danger comes before any click happens?
5. It can be hard to trace
By the time something is noticed, the chain of actors involved may be complex and opaque.
That combination makes it a serious digital rights issue, not just a technical one.
How to Protect Yourself
You cannot personally fix the ad-tech ecosystem, but you can reduce your exposure.
Practical steps:
- Use an ad blocker in your browser where possible.
- Choose a browser with strong tracker protection.
- Keep your phone and computer updated so security fixes are installed quickly.
- Turn off ad personalization in your device and account settings.
- Reset your mobile ad ID periodically if your device supports it.
- Remove apps you do not trust or do not use.
- Limit app permissions — especially location, microphone, camera, contacts, and background activity.
- Use separate devices or accounts for sensitive work if needed.
- Be extra careful on public Wi-Fi and with unfamiliar apps or websites.
- If you are at elevated risk, get advice from a digital security specialist.
A simple rule of thumb:
If an app or website feels like it is tracking too much, assume it may be collecting more than it admits.
What Publishers and Platforms Should Be Doing
This problem is not only on the user.
Websites, app developers, and ad-tech companies should be doing far more to reduce abuse.
That means:
- Better screening of advertisers
- Stronger vetting of intermediaries
- Clearer audit trails
- More transparency about who is buying and serving ads
- Faster abuse detection and removal
- Independent oversight instead of self-policing alone
The report’s bigger message is that the current system is too opaque. When systems are this complicated, bad actors can hide inside them.
And when nobody can clearly see what happens inside the ad supply chain, everyone becomes more vulnerable.
The Bigger Digital Rights Issue
This isn’t only about malware.
It is about power.
Who gets to watch whom?
Who gets to collect data?
Who gets to operate invisibly?
Who gets to decide what code runs on your device?
When online advertising becomes a surveillance channel, the line between marketing and monitoring starts to disappear.
That should concern anyone who values free expression, press freedom, or private life online.
If spyware can hide inside normal internet infrastructure, then digital rights are no longer just about what you post or click. They are about whether the systems around you are being weaponized against you.
Conclusion
The lesson from this research is simple but uncomfortable: ads are no longer just ads.
In some cases, they can be part of a surveillance pipeline.
That means the ad-tech industry needs far more transparency, accountability, and public scrutiny than it has today. Self-regulation is not enough when the risks include spyware, covert tracking, and silent compromise.
The internet should not force people to choose between using modern websites and protecting their safety.
Until ad systems become more transparent and more accountable, every targeted ad should be viewed with a little more caution — because behind the polished image, there may be a hidden mechanism watching back.

